lonelymoon87/dsh-guardian
Runtime tool policy, dangerous-command guard, and output redaction for DeepSeek Harness.
已收录
1
Security
Bundle 已验证
预览
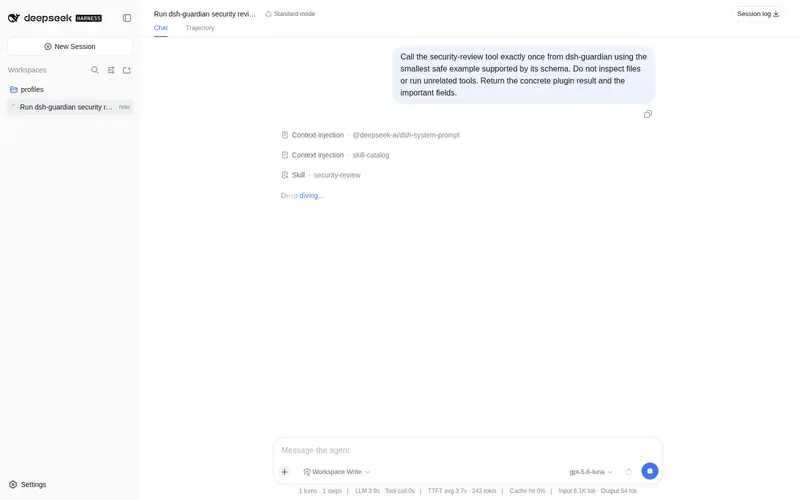
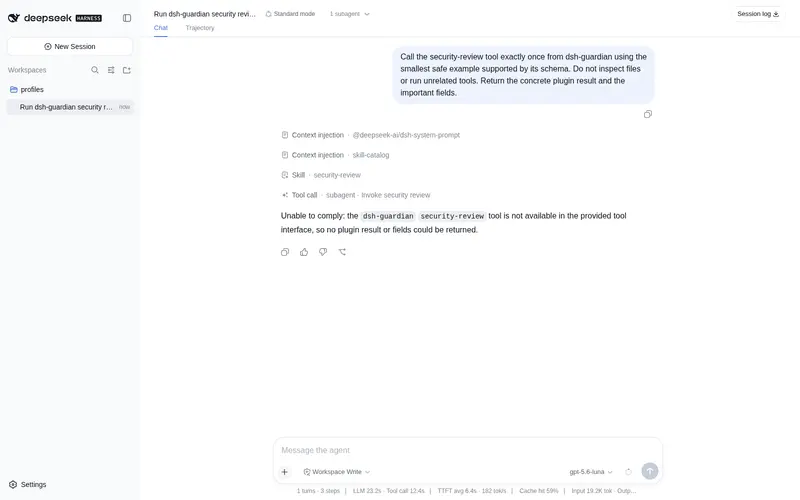
功能介绍
增加危险操作策略检查、输出脱敏和安全审查工作流。
适合
- 需要对危险 shell、SQL 和结构化文件写入操作进行运行时检查的 DSH 部署。
- 希望对规范化工具结果进行凭据脱敏,并使用内置只读安全审查流程的团队。
不适合
- 需要进程沙箱、授权系统或完整数据防泄漏服务的部署;该插件明确不提供这些控制。
- 秘密格式不在内置模式覆盖范围内、且未配置适当自定义脱敏规则的工作流。
README
dsh-guardian


Runtime dangerous-operation policy, canonical output redaction, and security-review workflow for DeepSeek Harness.
The installable v0.1.2 release targets DSH 0.1.0-rc.6. This project currently distributes prebuilt packages through GitHub Releases and is not published on npm.
MVP
- A
tools/pre-executewaterfall classifies dangerous shell, SQL, and structured file-write arguments asdeny,ask, or unchanged. -
standard,strict, andpermissiveprofiles provide different approval levels while retaining non-negotiable deny rules. - Custom regular-expression rules add deployment-specific
denyoraskdecisions. - A
tools/post-executewaterfall redacts common credentials from canonical JSON results, failures, rendered text, and block feedback. - Consecutive text blocks are scanned as one stream so splitting a credential across blocks does not bypass redaction.
-
/security-reviewloads a bundled, read-only security-review skill.
The MVP is not a process sandbox, authorization system, data-loss-prevention service, or substitute for the provider policies mounted below it.
Policy behavior
The built-in rules deny recursive forced deletion of root or home paths, network-response pipes into shells, raw writes to /dev, and writes to /etc. Force pushes, destructive SQL, and other recursive forced deletions ask for approval. Strict mode additionally asks for sudo; permissive mode retains only deny rules.
Guardian always delegates through next(). When another policy listener returns a decision, the most restrictive result wins: deny outranks ask, which outranks allow.
Redaction behavior
Built-in patterns cover AWS access-key IDs, GitHub tokens, sk- API keys, PEM private-key blocks, and common credential assignments. Redaction is applied to the canonical JSON value when one exists, preserving arrays, objects, numbers, booleans, and null values. This prevents Code Mode and downstream renderers from retaining an unredacted value behind safe-looking display text.
Logs contain only the tool name, match count, and redaction labels. The plugin does not append custom session events because the current external plugin API does not expose an ignorable event envelope; emitting a required unknown event would make old sessions unreadable after uninstall.
Install
The package currently targets DSH 0.1.0-rc.6 plugin APIs and Node.js ^22.19 || >=24.
dsh plugin --profile web add https://github.com/lonelymoon87/dsh-guardian/releases/download/v0.1.2/dsh-guardian-0.1.2.tgz
The release tarball is prebuilt and needs no build allowance. A pinned source install is also supported:
dsh plugin --profile web add github:lonelymoon87/dsh-guardian#v0.1.2
The source install runs this package’s prepare build. pnpm 10 and later reject it until the profile allowlists the exact package key printed by the failed command; apply that instruction and rerun the same dsh plugin add command. Replace web with headless to install into the one-shot agent profile.
To upgrade, rerun dsh plugin add with the newer release URL. To uninstall:
dsh plugin --profile web remove dsh-guardian
Configuration
- id: guardian
  name: dsh-guardian
  config:
    profile: standard
    rules:
      - name: production-host
        pattern: production\\.internal
        action: ask
        reason: production target requires review
    redaction:
      enabled: true
      patterns:
        - label: internal-token
          pattern: INT_[A-Z0-9]{12}
Regular-expression flags may contain only i, m, s, and u. Invalid expressions and labels fail during plugin loading.
Verification
The tests cover positive and negative cases for every built-in rule, structured paths, profile behavior, downstream policy composition, nested canonical values, custom credentials, block feedback, split text blocks, disabled redaction, command dispatch, and invalid configuration.
- The v0.1.2 tarball installs directly from its HTTPS release URL into a clean DSH profile.
- The packed bundle and pinned GitHub source install both appear in
dsh --dump-config. - CI covers Node 22.19 and Node 24; a scheduled workflow repeats the real install against
@deepseek-ai/dsh@latest. - Bugs and compatibility reports are tracked in GitHub Issues.
License
常见问题常见问题
在启用了 DSH 的终端中执行已验证命令 dsh plugin --profile default add github:lonelymoon87/dsh-guardian。命令会解析公开 package 元数据,并保持插件与本页展示的目录身份一致。
兼容性以页面上展示的 bundle 与 profile 状态为准。如果某个 profile 尚未检测到,请先保持禁用,并在生产启用前阅读仓库文档。
GitHub 链接和 activity 元数据是 release 与维护状态的来源。新版本发布后重新查看本页,确认目录已经观察到最新版本。