SARTHAK2511/dsh-cve-audit
Live CVE/supply-chain audit for your workspace's own dependencies (npm/pip/go), backed by OSV.dev. A DeepSeek Harness (dsh) Cordis plugin.
已收录
0
Security
Bundle 已验证
预览
功能介绍
面向你自己项目依赖(npm/pip/go)的实时 CVE/供应链审计,基于 OSV.dev,提供 `cve_audit` 工具,并支持在 lockfile 变化时自动重新扫描。
适合
- 需要检查自身依赖文件中已知漏洞的 npm、Python 或 Go 项目。
- 需要由 OSV.dev 支持的按需 `cve_audit` 工具的 agent。
- 适合在受支持 lockfile 变化后自动重新扫描的工作区。
不适合
- 审计 DSH 插件本身的场景;其明确范围是工作区项目依赖。
- 无法访问所配置 OSV 端点的离线环境。
- 要求实现已经过真实 DSH 环境验证的生产关键审计;项目自述仍是尚未实机验证的早期脚手架。
README
dsh-cve-audit
Live CVE / supply-chain audit for your project’s own dependencies — not the harness’s plugins.
Most existing dsh security plugins (dsh-plugin-vetting, dsh-plugin-sentinel, upstream-radar) audit the plugin ecosystem itself. None of them scan the dependency lockfiles of the codebase you’re actually working in. dsh-cve-audit fills that gap: it reads package-lock.json / requirements.txt / go.sum in the workspace, batch-queries OSV.dev (free, no API key), and reports known CVEs sorted by severity — as a real tool the agent can call, and optionally re-run automatically whenever a lockfile changes.
Install
dsh plugin add @dsh-plugins/dsh-cve-audit
Usage
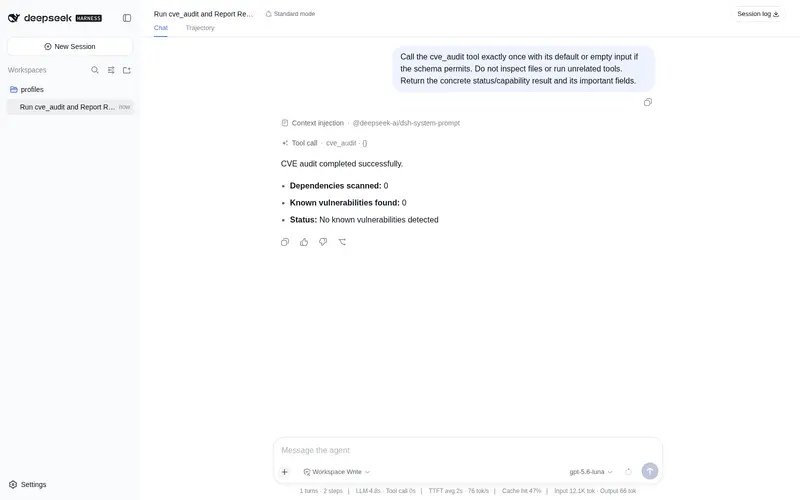
Ask the agent to “audit dependencies for CVEs” — it will call the cve_audit tool. Or trigger it directly:
cve_audit({ path: "." })
Config
watch: true          # re-scan automatically on lockfile changes
ecosystems: [npm, PyPI, Go]
osvEndpoint: https://api.osv.dev/v1/querybatch
Status
Early scaffold — built against the publicly documented Cordis plugin API (ctx.tools.register, defineTool, Schema.object, ctx.effect). Not yet run against a live dsh install; the lockfile watch currently uses Node’s fs.watch rather than a harness-native workspace-change event, since that event name isn’t in the public docs yet — swap in the native hook once confirmed. PRs welcome.
常见问题常见问题
在启用了 DSH 的终端中执行已验证命令 dsh plugin --profile default add github:SARTHAK2511/dsh-cve-audit。命令会解析公开 package 元数据,并保持插件与本页展示的目录身份一致。
兼容性以页面上展示的 bundle 与 profile 状态为准。如果某个 profile 尚未检测到,请先保持禁用,并在生产启用前阅读仓库文档。
GitHub 链接和 activity 元数据是 release 与维护状态的来源。新版本发布后重新查看本页,确认目录已经观察到最新版本。