TecFancy/dsh-auth-gate
Login gate for the DeepSeek Harness (dsh) web surface: password or shared-token authentication, session cookies, rate limiting, and a user-management CLI. | DeepSeek Harness (dsh) 网页版登录门插件:账号口令或共享令牌认证、会话 cookie、登录限速,附用户管理 CLI。
已收录
2
Security
Bundle 已验证
预览
功能介绍
DSH 网页端登录门插件:账号口令或共享令牌认证、会话 cookie、登录限速,附用户管理 CLI(0.4.1 起声明 dsh.bundle manifest,`dsh plugin add` 一键挂载)。
适合
- 适合需要对页面、API 和 WebSocket 统一鉴权的公开或共享 DSH Web 部署。
- 适合需要独立管理员账号、口令哈希存储、会话 cookie 和登录限速的团队。
- 适合可使用共享 Bearer token 认证的脚本客户端。
- 适合需要 CLI 用户管理,并要求配置异常时默认拒绝访问的运维人员。
不适合
- 不适合保护 DSH 的非 Web 接口,也不能替代操作系统和配置文件安全;插件只保护 Web 表面。
- 不适合要求禁用用户后立即撤销其现有会话的部署;禁用只会阻止新登录。
- 不适合在纯 HTTP 环境中仍启用 cookieSecure,浏览器会拒收安全会话 cookie。
- 不适合未经额外代理感知处理、却要求按真实客户端限速的反向代理部署;限速看到的是代理地址。
README
dsh-auth-gate
| English | 简体中文 |
A login door for your DeepSeek Harness (dsh) web instance. Put it in front of a public dsh deployment and nobody can reach your agents, your chat sessions, or your LLM credentials without signing in first.
What it does
-
Everything needs a login. Every page, API call, and WebSocket connection
is checked. Visitors without a valid session are sent to a simple login page
(or rejected with
401for API/script requests). -
Two ways to sign in (pick one in the configuration):
- Password (recommended): each admin gets a username and password.
- Token: one shared secret token for the whole instance.
-
Works for browsers and scripts. Browsers use the login page; scripts and
curl can pass
Authorization: Bearer <token>and skip the page entirely. - Safe by default. Passwords are stored hashed, logins are rate-limited (repeated wrong attempts temporarily lock the address), session cookies are secure, and any missing or broken configuration blocks access instead of silently opening the door.
-
A small command-line tool for managing users:
dsh-auth user add admin --password-stdin   # add a user
dsh-auth user list                          # list users
dsh-auth user disable admin                 # block a user's future logins
Quick start
# 1. Install the plugin from npm into your dsh profile.
#    Since 0.4.1 the package declares a `dsh.bundle` manifest, so `dsh plugin add`
#    also registers the mount (dsh.profile.bundles) automatically:
dsh plugin --profile web add dsh-auth-gate

# 2. Create an admin account
printf '%s\n' 'choose-a-strong-password' | dsh-auth user add admin --password-stdin

# 3. Turn on password login: override the plugin config in $DSH_HOME/cordis.patch.yml
#    (a ready-to-use config-override template ships in deploy/cordis.patch.yml;
#    see Configuration below — the mount itself needs no manual patch row)

# 4. Restart dsh. Open your site — you will be asked to sign in.
See it in action
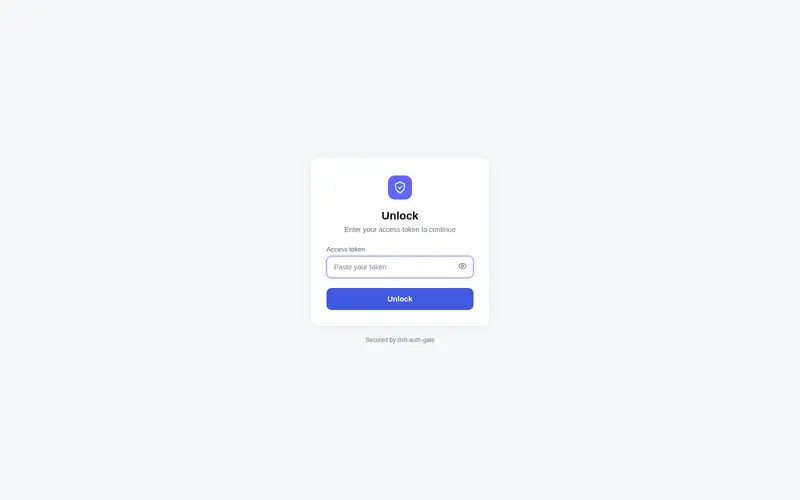
Visitors without a session are sent to the login page:

After signing in, they land on your instance:

A Sign out icon button sits at the top-right: inside a session, at the right of the Session log button in the session header; on the new-session page (no session open), at the window’s top-right corner. Icon-only, with a theme-aware hover background (light/dark follow the active theme), matching the header’s other icon buttons.
New-session page (no input/response yet):

Real conversation (session header, right of the Session log):

Configuration
The bundle mount (id dsh-auth-gate, inserted by dsh plugin add) uses the
default config: mode: "token" backed by the DSH_AUTH_TOKEN environment
variable. To change it, override the config in $DSH_HOME/cordis.patch.yml
(or the profile’s cordis.patch.yml — a ready-to-use override template ships
in deploy/cordis.patch.yml). The override targets the mounted row by id
(no insert — adding one would double-mount the plugin):
- id: dsh-auth-gate
  config:
    mode: "password" # "password" (recommended) or "token"
    cookieSecure: true # keep true when you use https
| Option | Default | What it does |
|---|---|---|
mode |
"token" |
"password" = username/password login; "token" = one shared secret |
sessionTtl |
604800 |
How long a login lasts (seconds) before you must sign in again |
cookieName |
dsh_auth |
Name of the session cookie (rarely needs changing) |
tokenRef |
"DSH_AUTH_TOKEN" |
Token mode only: which environment variable holds the shared secret |
cookieSecure |
true |
Set to false only if you are testing over plain http |
usersFile |
"" |
Password mode: where your user list lives. Defaults to $DSH_HOME/auth/users.yaml
|
Deployment
-
Reverse-proxy deployment guide — Caddy/nginx
setups, the browser-trust fence gotcha (Settings-page
403s behind a proxy, and why auth alone doesn’t fix them), and the recommended semi-shell topology. -
docs/deployment.md— ops checklist, acceptance steps (A–I) and troubleshooting. Chinese version:docs/deployment_zh.md.
Requirements
- Node ≥ 22.19 and pnpm on the server.
- The dsh
webprofile running (dsh --profile web). - If
cookieSecureistrue, your site must be served over https (browsers refuse secure cookies on plain http).
License
Notes & limitations
- Disabling a user only stops new logins; already-signed-in sessions stay valid until they expire.
- Login rate limiting resets when the server restarts.
- Behind a reverse proxy, rate limiting counts by the proxy’s address.
- Sign out from the GUI: a Sign out icon button sits at the top-right — in
the session header right of the Session log button inside a session, and at
the window’s top-right on the new-session page (client half, requires the
web app’s client bundle — dsh 0.1.0-rc.6+); the direct
/auth/logout?next=/URL always works as a fallback. - The plugin only protects dsh’s web surface. It is not a replacement for
server-level security: keep the server OS user locked down and the config
files private (
.credentials.yamlandauth/users.yamlare created with0600permissions).
常见问题常见问题
在启用了 DSH 的终端中执行已验证命令 dsh plugin --profile default add github:TecFancy/dsh-auth-gate。命令会解析公开 package 元数据,并保持插件与本页展示的目录身份一致。
兼容性以页面上展示的 bundle 与 profile 状态为准。如果某个 profile 尚未检测到,请先保持禁用,并在生产启用前阅读仓库文档。
GitHub 链接和 activity 元数据是 release 与维护状态的来源。新版本发布后重新查看本页,确认目录已经观察到最新版本。